
softu2f 0.4.0
 pool/sid/main/s/softu2f/softu2f_0.4.0_all.deb softu2f
| Filename | pool/sid/main/s/softu2f/softu2f_0.4.0_all.deb |
| Version | 0.4.0 |
| Age in days | 707 |
| Release date | 2024 11. 28. |
| Size | 2.34 KB |
| id | 881 |
| Name | softu2f |
| Package | |
| Appname | |
| Essential | |
| Vendor | |
| License | |
| Distribution | sid |
| Suite | main |
| Source | |
| Architecture | binary-i386 |
| MultiArch | |
| Maintainer | Daniel Stiner |
| InstalledSize | 9 |
| Depends | softu2f-user-daemon |
| PreDepends | |
| Breaks | |
| Enhances | |
| Section | unknown |
| Priority | optional |
| Description | U2F security token emulator written in Rust |
| LongDescription | |
| AutoBuiltPackage | |
| Filename | pool/sid/main/s/softu2f/softu2f_0.4.0_all.deb |
| MD5sum | 4e9e41df5869b7175c35b9831ad41788 |
| SHA1 | c32ed46f51a2369a937fe903422b1aed92f98b93 |
| SHA256 | 23b872df2c8df9998647539c5dee55fb68417e7cb766688fe5556831d3a21ab9 |
| SHA512 | 8ec1752c2cc773ddfcd0b5ac2e09dc34fdcfe1dc3f19f179d344866752df2869e1525fbaea9cea2f00c812c2e48d33f636fd2bfc555273e0f754ed1e6469362b |
| Size | 2392 |
| Auto-Built-Package | |
| Homepage | https://github.com/danstiner/softu2f-linux |
| Provides | |
| Existing | |
| fileMtime | 2024-11-28 12:35:02 |
| created | 2021-05-10 21:03:43 |
| updated | 2024-11-28 11:35:02 |
Rust U2F
A software-only Universal 2nd Factor token. Supports Google Chrome and Firefox on Linux. Written in Rust.
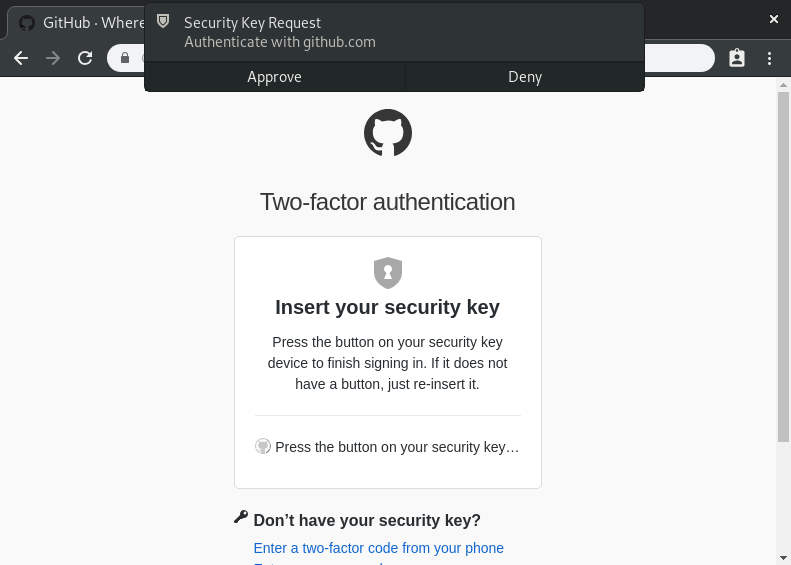
This program is basically complete, I am not currently planning to add new features like passwordless login the newer FIDO2 standard supports.
Security
Disclaimer: This is a personal project, I am not a security expert and make no guarantee of security.
Like any U2F authenticator this program provides a degree of protection against phishing and poorly chosen passwords. It does not provide the same level of protection against malware that a hardware authenticator does.
If your machine is compromised by malware, the attacker could steal a copy of the secret keys stored by this authenticator. In this situation you should immediately unregister this authenticator anywhere it is registered in addition to changing the passwords of any potentially compromised accounts. With a hardware authenticator secret keys never leave the device, so in the case of malware you can simply unplug from the infected machine and be confident your accounts are safe from further compromise.
Installation
After installing, test your new virtual U2F device on a site supporting it such as: https://demo.yubico.com/webauthn-technical/registration
Arch
Install the AUR package maintained by @grawity: https://aur.archlinux.org/packages/softu2f/
Then enable and start the installed services:
systemctl --system enable --now softu2f.socket
systemctl --user   enable --now softu2f.service
Fedora
curl -s https://packagecloud.io/install/repositories/danstiner/softu2f/script.rpm.sh | sudo bash
sudo dnf install softu2f
systemctl --system start softu2f.socket
systemctl --user   start softu2f.service
Ubuntu
sudo apt install -y curl
curl -s https://packagecloud.io/install/repositories/danstiner/softu2f/script.deb.sh | sudo bash
sudo apt install -y softu2f
systemctl --system start softu2f.socket
systemctl --user   start softu2f.service
Building
See Dockerfile.debian or Dockerfile.fedora for pre-requisite packages that must be installed.
Then run cd linux && make.
To install run cd linux && make install. The install target uses sudo so you will be prompted for your password.
Bump version
- Run
bumpversion --no-tag patch - Update
linux/meta-package/debian/changelogand amend the commit - Push and manually tag the release
- Package for all platforms and upload package files
License
This project is licensed under either of
- Apache License, Version 2.0, (LICENSE-APACHE or http://www.apache.org/licenses/LICENSE-2.0)
- MIT license (LICENSE-MIT or http://opensource.org/licenses/MIT)
at your option.
Contribution
Unless you explicitly state otherwise, any contribution intentionally submitted for inclusion by you, as defined in the Apache-2.0 license, shall be dual licensed as above, without any additional terms or conditions.